Why Tracenyx exists, who's behind it, and how to reach us.
Tracenyx builds Nyx — a kernel-native network security and observability platform for Kubernetes. Nyx enforces zero-trust network policy and captures flow-level visibility at the kernel on both Linux nodes (eBPF) and Windows Server nodes (a Microsoft HLK-certified WFP callout driver), with one policy model and matched enforcement behaviour across both operating systems.
If Kubernetes networking isn't your day job, our plain-language guide to why Nyx exists covers the whole argument — the default nobody chose, how attackers use it, and what microsegmentation changes — with no Kubernetes expertise assumed.
We think evaluating security tooling should come before installing it. That's why Nyx has a public live demo — a real cluster you can explore with no signup at orbit.tracenyx.ai — and a free tier you can install with one Helm command.
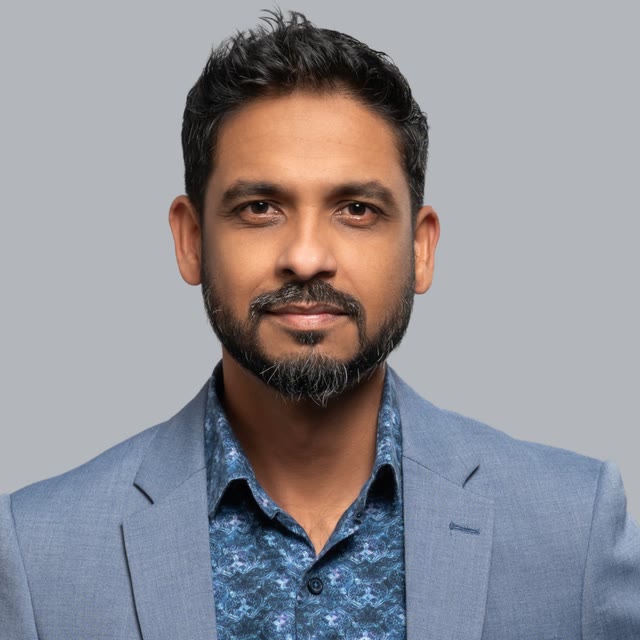
Ishara has spent twenty years across software development, DevOps, and platform engineering, including leading enterprise container platforms in regulated industries. He founded Tracenyx in Melbourne, Australia, to close a gap he kept meeting in practice: kernel-level network security and observability that treats Windows Server nodes as first-class citizens alongside Linux.
Tracenyx is founder-led, supported by a small engineering team.
Tracenyx Pty Ltd
Registered in Australia (ASIC) · ABN 77696388879
Melbourne, Victoria, Australia
Member of Microsoft for Startups, AWS Activate, and NVIDIA Inception.